Skip to content
Governance

AI governance platform with runtime enforcement

An AI governance platform has to do more than document intent: it has to enforce it at runtime and prove it afterwards. In Skyfix policy ships as signed bundles, change passes approval, every AI system is inventoried, and framework assessments cite the same ledger that recorded each decision.

  • Signed runtime bundles
  • Verifiable decision ledger
  • Framework assessments
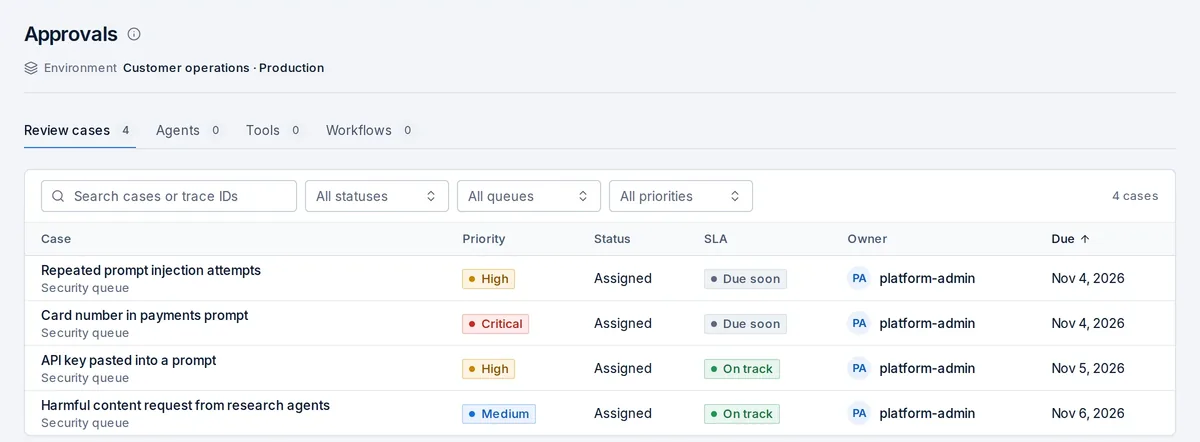
The Governance › Approvals page of the Skyfix console: review cases opened from AI Firewall findings, each with a priority, an owner, an SLA and a due date.The Governance › Approvals page of the Skyfix console: review cases opened from AI Firewall findings, each with a priority, an owner, an SLA and a due date.
Review cases. Firewall findings become review cases with a priority, an owner, an SLA and a due date.Illustrative synthetic data

One control plane

Where this sits in the request path

Policy is evaluated locally by each gateway from a verified bundle; the control plane never dials a gateway at request time.

  1. Identity

  2. Policy

  3. AI Firewall

  4. Budget

  5. Route

  6. Evidence

01

Policy that ships as signed bundles

  • Scoped fan-out
  • Compatibility

Every management decision, from allowed models and regions to MCP tool approvals, A2A partners, prompts, budgets and telemetry settings, compiles into one runtime bundle. The bundle is signed under your installation's own key, delivered to exactly the gateways it targets, and verified by each gateway before it is applied. Publication is a durable intent: a publish that is interrupted resumes rather than leaving half a fleet on the old policy.

Because gateways hold a verified copy, policy keeps working when the control plane is unreachable. For incidents there is an emergency deny switch and a last-known-good bundle, so a fleet can be frozen or rolled back in one signed action.

02

Approvals and review cases

High-impact changes wait for a second person. Approval queues cover policy publication, protected prompt labels, production promotion and tool catalog changes, and each approval is recorded with the approver, the time and what exactly was approved. AI Firewall findings open review cases with a priority, an owner, an SLA and a due date, so a detected injection attempt or a leaked secret becomes a tracked piece of work rather than a log line.

03

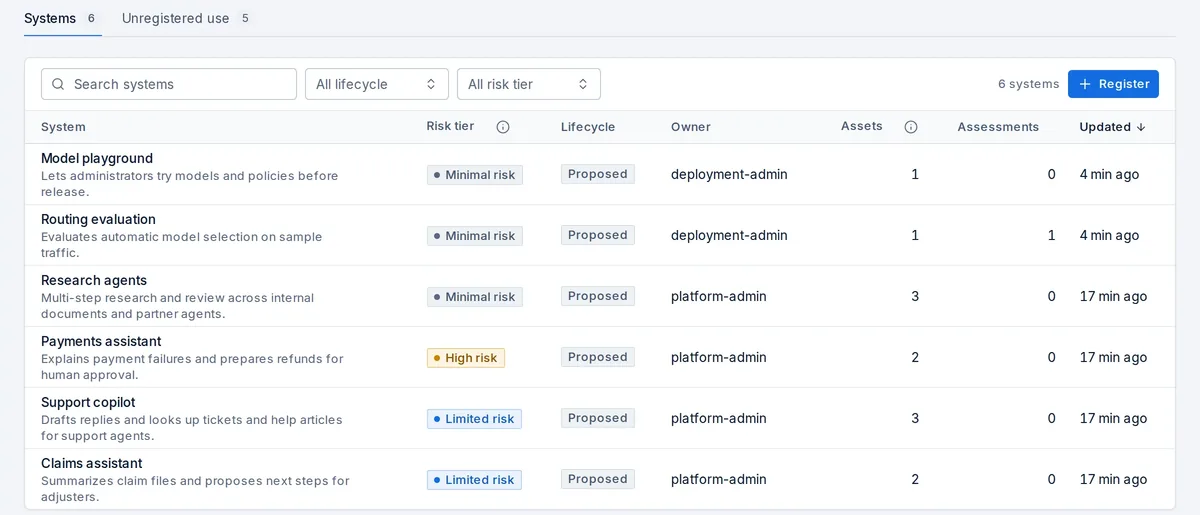
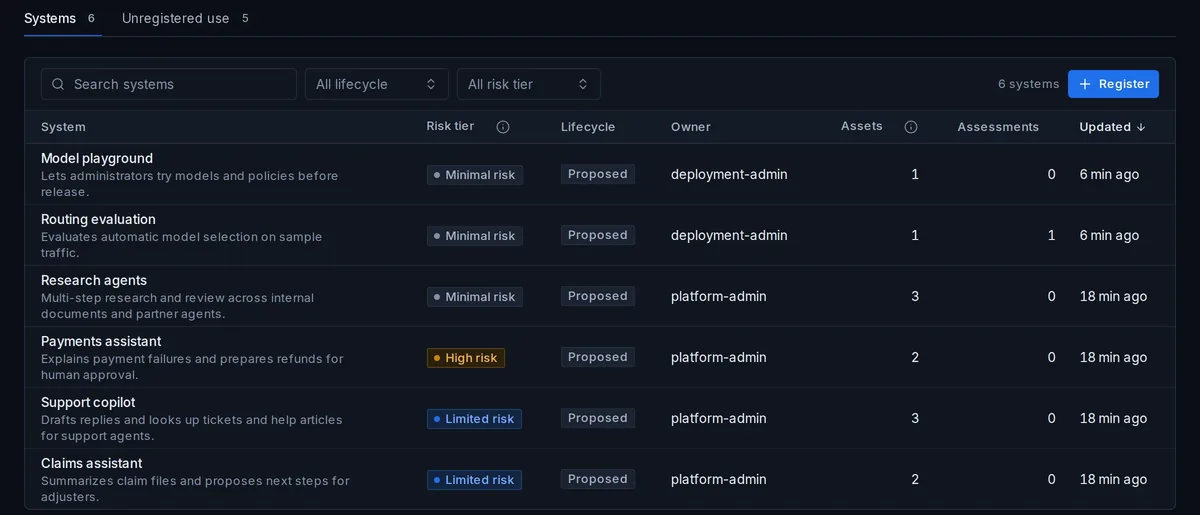
AI system inventory

Each AI system you register links to the keys, models, tools, workflows, agents and skills it uses, with an owner, a lifecycle stage and a risk tier. Readiness reads the live security posture of those linked assets: an open critical or high finding blocks readiness, lower findings call for attention, and the posture score and finding list sit on the system's own page for anyone with permission to see them.

Obligations with due dates roll up per system, so the inventory answers both 'what do we run?' and 'what is due?'.

Framework assessments support evidence for frameworks such as the NIST AI RMF, ISO/IEC 42001 and the EU AI Act. They are not certifications, attestations or compliance scores.

The Governance › AI systems inventory in the Skyfix console: registered AI systems with their owner, lifecycle stage, linked assets and risk tier.The Governance › AI systems inventory in the Skyfix console: registered AI systems with their owner, lifecycle stage, linked assets and risk tier.
AI system inventory. AI systems registered with an owner, lifecycle, linked assets and a risk tier. The inventory supports evidence for risk classification under frameworks such as the EU AI Act; it is not a certification.Illustrative synthetic data

04

Framework assessments

Assessments are internal templates mapped to frameworks such as the NIST AI RMF, ISO/IEC 42001 and the EU AI Act. Each control in an assessment links to the platform evidence that supports it: a policy bundle, a ledger checkpoint, an audit export, an inventory entry. That makes an assessment a working document for your own risk and audit teams, with evidence attached. It is not a certification, an attestation or a compliance score, and Skyfix does not claim one.

Framework assessments support evidence for frameworks such as the NIST AI RMF, ISO/IEC 42001 and the EU AI Act. They are not certifications, attestations or compliance scores.
05

Prompt registry, retention and legal hold

  • Protected labels
  • Retention

Prompts are governance objects: named, versioned, labeled, promoted and rolled back with an audit entry each time, and rendered by the gateway before inspection so a prompt change gets the same guardrails as any request. Retention is configured per workspace for traces, content and audit records, and a legal hold suspends deletion for the records it names until it is lifted.

06

Ledger and audit

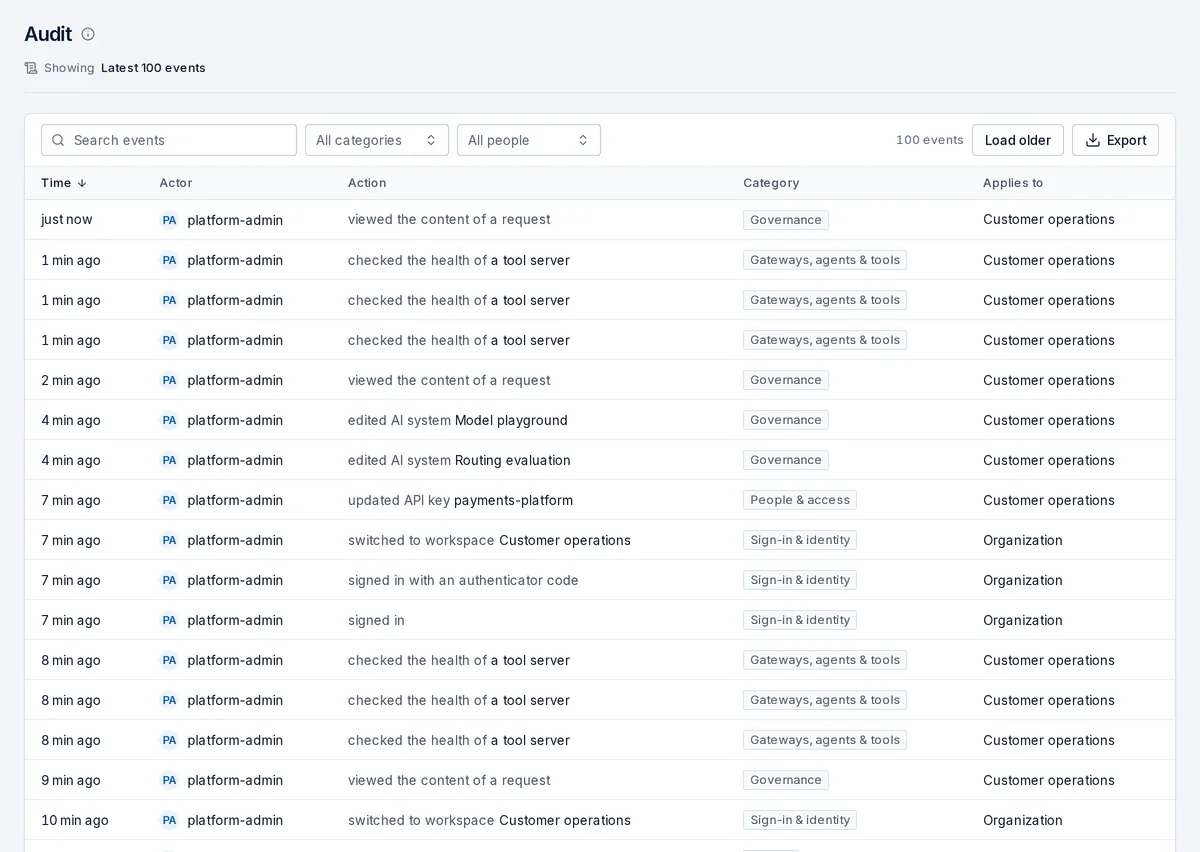
Every governed decision across LLM, MCP and A2A traffic lands in one hash-chained ledger with signed checkpoints. Every administrative action is recorded in plain language with actor, category and scope, in the same transaction as the action itself. Signed exports verify offline with nothing more than the export and your installation's root fingerprint.

The Governance › Audit page of the Skyfix console: a list of administrative actions described in plain language, each with the actor, category, scope and time, with filters and an export control.The Governance › Audit page of the Skyfix console: a list of administrative actions described in plain language, each with the actor, category, scope and time, with filters and an export control.
Audit trail. Administrative actions recorded in plain language with actor, category and scope, ready to export.Illustrative synthetic data

Framework assessments support evidence for frameworks such as the NIST AI RMF, ISO/IEC 42001 and the EU AI Act. They are not certifications, attestations or compliance scores.
FAQ

Questions this page answers

What does an AI governance platform do?

It turns policy into something enforced at runtime and provable afterwards: signed policy bundles, approvals for high-impact change, an inventory of AI systems with their risk tier and readiness, and assessments that cite recorded evidence. Skyfix does all of this from one console and one ledger.

How does policy reach the gateways?

As a signed runtime bundle the control plane compiles and delivers to the gateways it targets. Each gateway verifies the signature before applying the bundle and keeps the last good one if a new one cannot be verified.

Does Skyfix certify compliance?

No. Framework assessments support evidence for frameworks such as the NIST AI RMF, ISO/IEC 42001 and the EU AI Act. They are internal templates linked to platform evidence, not certifications, attestations or compliance scores.
How are AI systems registered and tiered?

An AI system is registered with an owner, a lifecycle stage and a risk tier, and linked to the keys, models, tools, workflows, agents and skills it uses. Its readiness reads the open security posture findings of those linked assets.

Who can approve high-impact changes?

Roles with the matching write permission at the organization or workspace level, and only after step-up re-authentication. Approvals are recorded with the approver, the time and the exact change.